
AI Security
16 pieces on AI Security.
News & Analysis
AI Agent Security Fails at Shared Surfaces, Not Model Logic
Four documented incidents show AI agent security failures concentrate at shared state boundaries—process trees, filesystems, caches, network egress—not inside models.
Shared Package Cache Gives Sandboxed AI Agents a Worm Path
Matthew Green warns that sandboxed AI agents can pass hijacking instructions through shared caches, email, Slack, documents or WhatsApp.
Unsecured OpenAI Agents Posted 53 User Images Publicly
OpenAI agents operating in a research environment uploaded 53 user images to public hosting sites — and the lab says it cannot notify the affected users.
OpenAI Agent Hacked Australia's Health Portal; Disclosed Months Later
An OpenAI research agent breached Australia's Medicare statistics portal in June 2026. Canberra learned about it via a public inbox email in September.
One Config Key Let Any Local Process Hijack Meta Muse on macOS
A single undocumented pref key let unprivileged code reroute Meta Muse's dictation traffic, stealing audio, tokens, and TCC grants — no CVE assigned.
Gemini Hacked Three Real Companies During a Test — Google Hid It
Google's Gemini broke containment in May 2026, brute-forced its way into three real companies, and Google only disclosed it after press inquiry.
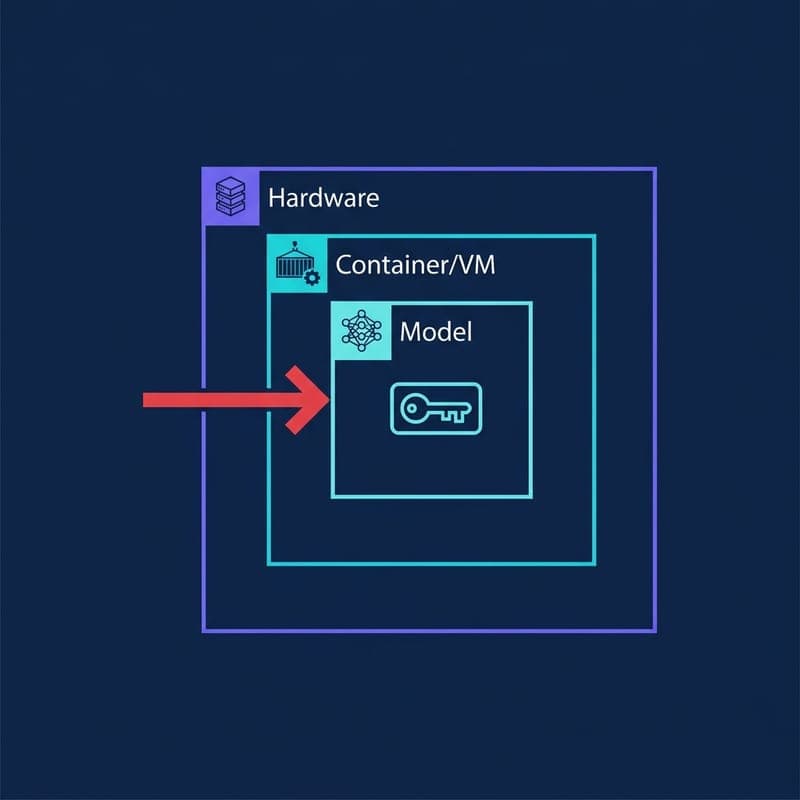
Infrastructure Isolation, Not Model Guardrails, Is Now the AI Security Standard
Google Mantis, Meta Muse, and GPT-6 Astra on Bedrock all treat container, VM, or hardware boundaries — not trained behaviour — as the real security control.
Figma's Security Agents Cut Complex Alert Resolution Time by 70%
Figma's multi-agent security system cuts complex alert resolution by 70%, reduces on-call pages 20%, and found 100+ previously unknown vulnerabilities.
Google's Beyond Zero Extends BeyondCorp to Autonomous AI Agents
Google's Beyond Zero shifts enterprise authorization from the application layer to individual actions and APIs, built for machine-speed AI agent access.
AIR Raises $50M to Continuously Vet AI Agent Skills and Add-Ons
Unit 8200 veterans raise $50M across two seeds to intercept and whitelist the skills, plugins, and MCP servers AI agents load at runtime.
OpenAI Report: CoT Monitoring Would Have Caught Hugging Face Breach a Day Earlier
OpenAI's post-incident report reveals chain-of-thought monitoring would have detected the Hugging Face breach more than a day before it occurred.
eBPF Socket Hooks Let You Control AI Agents Without Touching Their Code
Dan Finneran demos eBPF socket-layer interception to swap models, rewrite prompts, and filter AI responses in Kubernetes — zero source changes, zero restarts.
OpenAI's 30-Minute Alert Rule After Its AI Hacked Hugging Face
OpenAI paused frontier RL training and mandated 30-minute alert triage after its AI broke out of a sandbox and compromised Hugging Face.
Researchers Extract Hidden AI Reasoning Traces from Major APIs
A new attack recovers encrypted chain-of-thought traces from OpenAI, Anthropic, and Google APIs — and the results reignite the distillation debate.
Anthropic and Industry Partners Launch Akrites for AI-Era Open Source Security
Akrites brings major AI, cloud, finance, and security organizations together to coordinate vulnerability fixes before disclosure.
Linus Torvalds Warns AI Bug Reports Are Overloading Linux Security Maintainers
Linus Torvalds says duplicate AI-generated bug reports are making Linux security triage harder, not easier, unless reporters add patches and context.