
Claude Watermarks: Inspect Provenance and Preserve Working Code
In this article
- Step 1: Identify the question before choosing a tool
- Step 2: Preserve the original before making a derivative
- Step 3: Edit prose for accuracy and readability
- Step 4: Refactor code with scope and behavior checks
- Step 5: Read local C2PA data without changing the media
- Step 6: Review the report's assertions and limitations
- Step 7: Keep transformation and inspection records separate
A useful provenance workflow preserves the material being assessed and records what each check actually establishes. Text watermark detection, signed media credentials and an editorial review answer different questions. This guide provides a local media-inspection example and a procedure for editing prose or code without confusing those activities with detection.
Correction, 22 October 2026: The earlier guide presented a generic rewrite and Python renaming routine as watermark-handling techniques without a detector evaluation. The renamer can break ordinary programs, and its C2PA example collapsed every error into a missing-manifest result. Those examples are withdrawn. The replacement below reads local manifest data and reports uncertainty explicitly. The original URL is retained so readers following an older link reach this correction.
Step 1: Identify the question before choosing a tool
Anthropic describes Claude's text watermark as a pattern in word choices detectable with a provider key, without added hidden characters. It indicates likely Claude involvement, not a particular user. The explanation describes its detection API as a private preview and distinguishes it from tools that infer AI use from writing style. Those statements do not establish that every historical Claude output has the same marking.
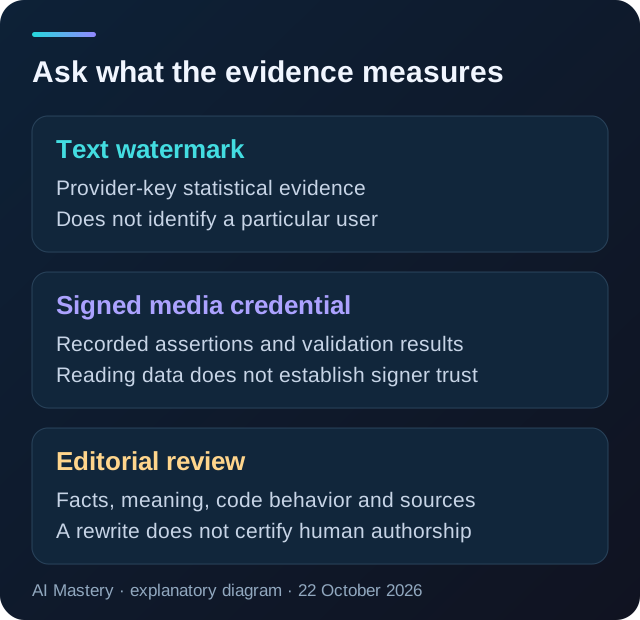
| Your question | Relevant evidence | What the result cannot establish alone |
|---|---|---|
| Was Claude likely involved in this text? | A provider-key detection result with its scope | The identity of a writer or user |
| What provenance is recorded for this media? | Manifest assertions and validation details | The truth of every depicted event |
| Is this draft accurate and readable? | Source review and editorial comparison | Whether a watermark is detectable |
| Does a code edit preserve behavior? | Tests and interface checks | The origin of the source code |
Step 2: Preserve the original before making a derivative
Keep the original file and work on a separate copy. Record its filename, where it came from and the tool versions used to inspect it. A SHA-256 fingerprint can identify the exact bytes assessed later; it is not an authorship detector. The example below records that fingerprint and checks that the input bytes remain unchanged during inspection.
Keep any report with the original material. A result copied into an email without the input identity and tool settings can be difficult to interpret when a different file is supplied later. Avoid overwriting the original with an edited or re-exported version.
Step 3: Edit prose for accuracy and readability
An editorial pass should preserve numbers, quotations, citations and the meaning of each claim. If an edit changes a claim, resolve that difference against the source rather than accepting more fluent wording as evidence of correctness.
A Humanizer-style pass can help identify repetitive phrasing and inflated claims. It does not run a provider's keyed detector. This guide has performed no watermark-removal experiment, and it does not certify that a rewrite will pass any detector. Use the editor preservation method to compare factual content before and after a rewrite.
Step 4: Refactor code with scope and behavior checks
The previous Python AST example renamed every Name node, including built-ins, while leaving other identifiers outside that traversal unchanged. It also deleted a leading docstring without ensuring a function retained a valid body. In two synthetic fixtures executed on Python 3.14 during this correction, the first behavior produced a NameError and the second an IndentationError.
For example, renaming the reference in print("hello") without providing the replacement function leaves an unresolved name. A function containing only a docstring needs a valid statement after that docstring is removed. Parsing and regenerating an AST does not by itself preserve program behavior.
Anthropic's explanation says exact code constraints leave fewer choices for watermarking. That is not a reason to rename APIs or strip comments indiscriminately. For a legitimate refactor, use language-aware tooling, keep public contracts stable and run relevant tests before and after the change. The generic renamer is no longer offered as a runnable solution.
Step 5: Read local C2PA data without changing the media
Anthropic distinguishes supported media-file credentials from its text watermark. For inspection, the Content Authenticity Initiative's Python SDK provides Reader and Context; its settings reference controls verification and remote resource behavior.
The example is tested with Python 3.14.0 and c2pa-python 0.38.0 on Windows. Use a virtual environment, then download inspect-c2pa.py and run it against a local asset. The SDK's published prerequisite is Python 3.10 or later, but this review tested only the stated version and platform.
python -m venv .venv
Use the virtual environment's Python executable for the following commands. On Windows that is .venv\Scripts\python.exe; on macOS or Linux it is .venv/bin/python. Replace python accordingly after creating the environment.
python -m pip install c2pa-python==0.38.0
python inspect-c2pa.py image.jpg
The complete reader is below. It disables remote-manifest and OCSP fetching in the SDK settings. It deliberately does not establish signer trust or issue an authorship verdict. Reading JSON successfully is recorded separately from an inconclusive inspection.
"""Read local C2PA data without transforming the input or deciding authorship.

Requires c2pa-python==0.38.0. Exit 0 means a report was read, not that
the signer is trusted or the asset is human-created. Exit 2 is inconclusive.
"""

import argparse
import hashlib
import json
from pathlib import Path
import sys

from c2pa import Context, Reader


def sha256_file(path: Path) -> str:
    digest = hashlib.sha256()
    with path.open("rb") as source:
        for chunk in iter(lambda: source.read(65536), b""):
            digest.update(chunk)
    return digest.hexdigest()


def inspect_file(path: Path) -> dict:
    before = sha256_file(path)
    try:
        with Context.from_dict({
            "verify": {
                "remote_manifest_fetch": False,
                "ocsp_fetch": False,
                "verify_trust": False,
                "verify_timestamp_trust": False,
            }
        }) as context:
            with Reader(str(path), context=context) as reader:
                manifest_store = json.loads(reader.json())
        result = {
            "status": "manifest_report_read",
            "manifest_store": manifest_store,
        }
    except Exception as error:
        result = {
            "status": "inconclusive",
            "error_type": type(error).__name__,
            "error": str(error),
        }

    after = sha256_file(path)
    if before != after:
        raise RuntimeError("Input bytes changed during inspection")
    return {
        "file": path.name,
        "sha256": before,
        "input_unchanged": True,
        "scope": "Local manifest inspection; signer trust is not established; no authorship verdict",
        **result,
    }


def main() -> int:
    parser = argparse.ArgumentParser(description=__doc__)
    parser.add_argument("asset", type=Path)
    args = parser.parse_args()
    try:
        result = inspect_file(args.asset)
    except (OSError, RuntimeError) as error:
        result = {
            "status": "inconclusive",
            "error_type": type(error).__name__,
            "error": str(error),
        }
    print(json.dumps(result, ensure_ascii=False, indent=2))
    return 0 if result["status"] == "manifest_report_read" else 2


if __name__ == "__main__":
    sys.exit(main())
Do not interpret exit code zero as "the signature is trusted" or "this is human-made." It means the example obtained a manifest report. Exit code two means the inspection is inconclusive; retain the error rather than converting it into a claim that no provenance exists.
Step 6: Review the report's assertions and limitations
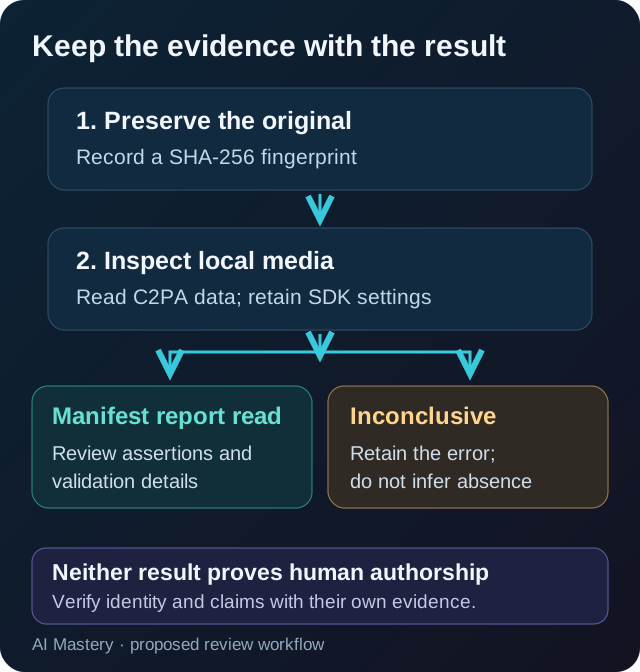
The SDK can return validation information within the manifest store. Examine it along with the recorded assertions and the configuration used. A credential identifying an editing application is not a guarantee that all depicted content is true, and a parsed credential is not proof that its signer is trusted under your organization's policy.
This example disables signer and timestamp trust checks and supplies no trust anchors. It is a diagnostic reader, not a production trust-policy implementation. Remote manifests are not fetched, so that setting can also limit what is available to inspect. To perform a trust assessment, follow the SDK's trust configuration documentation and retain the resulting validation report; do not infer that assessment from this example's status field.
Step 7: Keep transformation and inspection records separate
If you produce a derivative, preserve a link to the original and record what changed. Inspect that derivative separately. A screenshot, conversion or re-save does not by itself establish what provenance survived, what was lost or what the content's origin was.
For this reader, five local cases were checked: a CAI fixture with readable manifest data, a fixture with no readable manifest, corrupt input, an unsupported text file and a missing path. The readable fixture returned a manifest report; the other four returned inconclusive results. Every existing input retained the same SHA-256 fingerprint. These checks validate those reader behaviors, not watermark detection, general signature trust or every supported media format.
The earlier renamer's two failures and this reader's five cases are documented in the guide verification record. Apply the same habit to future edits: record the specific behavior verified and keep the unanswered question visible.
Frequently asked questions
Does rewriting text prove a watermark has been removed?
No. This guide provides no provider-key detector test and makes no removal guarantee. A style edit is not an authorship verdict.
Can the original generic Python identifier renamer preserve arbitrary programs?
No. Two local fixtures reproduced a NameError from renaming print and an IndentationError after deleting a function's only docstring. That example has been withdrawn.
Does reading a C2PA manifest establish trusted authorship?
No. The example reads manifest data with signer-trust checking disabled. Review the assertions, validation results and trust configuration separately.
Does an inspection error mean the file has no provenance?
No. The example reports errors as inconclusive and exits with code 2. Missing data, unsupported input and read failures must not become a human-authorship claim.
Related Guides
Claude Watermarks: Two Systems, Three Output Types, One Gap
Claude uses SynthID-Text for prose and signed C2PA metadata for images — but code sits in a weak middle ground with fewer statistical degrees of freedom.
Build a Multi-Tool Claude Agent with MCP Servers in Python
Wire Claude to a local calculator, Brave search MCP server, and Anthropic-hosted tools in one extensible Python agent loop.
Anthropic Explains How Claude's SynthID-Text Watermarks Work
Anthropic details Claude's SynthID-Text watermarking: how it survives edits, why code gets negligible signal, and what a detection API means for developers.